Latest
School app Canvas breach hits during finals

Finals week is stressful enough without your school’s main classroom app suddenly going dark.
That is what many students faced when Canvas, the school platform used by colleges, universities and K-12 schools, went down for several hours. The outage came after Instructure, the company behind Canvas, detected unauthorized activity tied to a cybersecurity incident on the platform.
For students and teachers, this was more than a tech glitch. Canvas is where many schools post assignments, messages, grades, class updates and exam instructions. So when access disappeared, it created confusion at the worst possible time.
Sign up for my FREE CyberGuy Report
WHY LAST YEAR’S BREACH IS THIS YEAR’S IDENTITY FRAUD
Instructure says it detected unauthorized activity in Canvas on April 29, 2026. The company said it immediately revoked the unauthorized party’s access, started an investigation and brought in outside forensic experts.
Then, on May 7, Instructure said it identified additional unauthorized activity tied to the same incident. The company said the unauthorized actor made changes to pages that appeared when some students and teachers were logged in through Canvas.
Out of caution, Instructure temporarily took Canvas offline into maintenance mode to contain the activity, investigate and apply additional safeguards.
Instructure said it later confirmed that the unauthorized actor exploited an issue related to its Free-For-Teacher accounts. The company said this was the same issue that led to the unauthorized access the prior week.
In a statement to CyberGuy, Instructure said, “Instructure discovered the unauthorized actor involved in our ongoing security incident made changes to the pages that appeared when some students and teachers were logged in. Out of an abundance of caution, we immediately took Canvas offline to contain access and further investigate. We have confirmed that the unauthorized actor exploited an issue related to our Free-For-Teacher accounts. As a result, we have made the difficult decision to temporarily shut down our Free-For-Teacher accounts. This gives us the confidence to restore access to Canvas, which is now fully back online and available for use. We regret the inconvenience and concern this may have caused.”
That detail is important because it explains how the company says the attacker gained access. It also shows why Instructure took a more aggressive step after the May 7 activity.
The timing made the outage especially frustrating. Students across the country are preparing for finals or already taking them.
Several schools reported problems with Canvas access. Student newspapers at Harvard, the University of Pennsylvania, Duke, UCLA and the University of Nebraska were reportedly blocked from using Canvas and saw a message from the hacking group ShinyHunters.
Think about how that feels if you are a student. You may need to submit a paper, check exam details or message a professor. Then the system you rely on suddenly stops working.
That is the real-life problem with school tech. When one major platform goes down, the disruption spreads fast.
A hacking group called ShinyHunters claimed responsibility for the attack. The group reportedly threatened to leak school data unless it heard from affected schools by May 12, 2026.
The group also claimed it had data tied to nearly 9,000 schools and about 275 million people. Those numbers come from the hackers’ claims. Instructure has not publicly verified that full scale.
That is worth keeping in mind. Cybercriminals often use big numbers to create panic and pressure victims. However, the confirmed incident is serious enough for schools and families to pay attention.
Based on Instructure’s investigation so far, the data taken in the April 29 incident includes certain personal information of users at affected organizations. That includes names, email addresses, student ID numbers and messages among Canvas users. Instructure said it has found no evidence that passwords, dates of birth, government identifiers or financial information were involved.
The company also said that, based on its investigation to date, it has not found evidence that data was taken during the May 7 activity. Still, Instructure said the investigation is ongoing.
Even so, this kind of information can still create problems. A scammer could use a student’s school email and Canvas details to send a fake message that looks official.
For example, a student may get an email that says a final exam file failed to upload. Another message may claim the student needs to verify a Canvas account. A fake IT alert could ask for a login code. That is how a data breach can turn into a phishing attack.
Yes. Instructure says Canvas is fully back online and available for use. However, Free-For-Teacher accounts remain temporarily shut down while the company works through the issue.
The company also says its outside forensic partner reviewed the known indicators and found no evidence that the threat actor currently has access to the platform.
Instructure says it has revoked privileged credentials and access tokens tied to affected systems. It also says it deployed additional platform protections, rotated certain internal keys, restricted token creation pathways and added monitoring across its platforms.
Many parents may not know how much school life now runs through platforms like Canvas. Students use Canvas to track deadlines, get teacher updates, submit work and read class messages. Teachers use it to manage assignments and communicate with students.
That makes Canvas a tempting target. If criminals can disrupt access or steal user information, they can create chaos quickly. The bigger lesson here is that school accounts deserve the same protection as bank accounts or email accounts. They hold personal details, private messages and information tied to a student’s daily life.
HACKERS THREATEN TO LEAK DATA FROM 275M USERS AFTER BREACHING MAJOR COLLEGE PLATFORM USED NATIONWIDE
Even if passwords and financial details were not part of the breach, students and teachers should still stay alert. Scammers can use names, school emails, student ID numbers and message details to make fake alerts look convincing.
Be careful with any message that claims to come from Canvas, Instructure or your school’s IT department. Scammers may use urgent language. They may say your account will be locked, your exam file is missing, or your final grade is at risk. That pressure is the trick. Go directly to your school’s official website or Canvas login page instead of clicking links in surprise emails.
Instructure said it found no evidence that passwords were involved. Even so, follow your school’s instructions. If your school tells you to reset your password, do it right away. Choose a strong password you do not use anywhere else. A password manager can help you create and store unique logins for each account. Check out the best expert-reviewed password managers of 2026 at CyberGuy.com.
If your school offers multifactor authentication, turn it on. MFA adds another step when someone tries to log in. That extra step can stop a scammer who has your password. An authenticator app or passkey is stronger than a text code. Still, any MFA is better than leaving your account wide open.
No real school IT worker should ask for your password or login code. If someone asks for that information, treat it as a red flag. End the conversation and contact your school through an official help desk number or website.
Since Canvas messages may have been involved, think about what you shared there. Did you send personal details? Did you mention another account? Did you share private information with a teacher or classmate? You do not need to panic. But you should stay alert for messages that reference details from your Canvas account.
A breach like this can lead to phishing emails with malicious links or attachments. Strong antivirus software can help block malware, warn you about dangerous websites and protect your devices if you accidentally click the wrong link. Keep it updated on your phone, tablet and computer. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android and iOS devices at CyberGuy.com.
Student and teacher information can end up on people-search sites and data broker databases. A data removal service can help reduce how much personal information is floating around online. That can make it harder for scammers to connect your school email, home address, phone number and other personal details. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting CyberGuy.com.
If your school confirms that your personal information was involved, identity theft protection can help you spot suspicious activity faster. These services can monitor your personal information, alert you to possible misuse and help you respond if someone tries to use your identity. See my tips and best picks on Best Identity Theft Protection at CyberGuy.com.
Younger students may not recognize a fake school message. Parents should keep the warning simple. Tell students not to click unexpected links, share codes or respond to scary messages without checking first. A quick conversation now can prevent a bigger mess later.
Instructure says it notified impacted organizations on May 5, 2026. If a school or institution was affected, Instructure says it will contact that organization’s primary contacts directly.
For students, parents and employees, Instructure says the school or institution should be the first point of contact. It also recommends being cautious of unexpected emails or messages about the incident, avoiding suspicious links and reporting anything unusual to the school’s IT or security team.
Schools should also warn students and staff about follow-up scams. A breach does not end when the platform comes back online. For students and teachers, the risk can continue through fake emails, fake login pages and scam messages.
ADT DATA BREACH EXPOSES CUSTOMER INFORMATION
The Canvas breach shows how much school now depends on a few digital platforms. When one of them goes down, students feel it right away. The good news is that Instructure says it has found no evidence that passwords, financial data, birthdays or government IDs were involved. The tougher reality is that names, school emails, student IDs and private messages still have value to scammers. So the best move is to stay calm and stay skeptical. Use official school links. Turn on stronger login protection where possible and treat urgent messages with caution.
Should schools and tech companies do more to protect student and teacher data before a breach puts their privacy at risk? Let us know by writing to us at CyberGuy.com.
Sign up for my FREE CyberGuy Report
Copyright 2026 CyberGuy.com. All rights reserved.
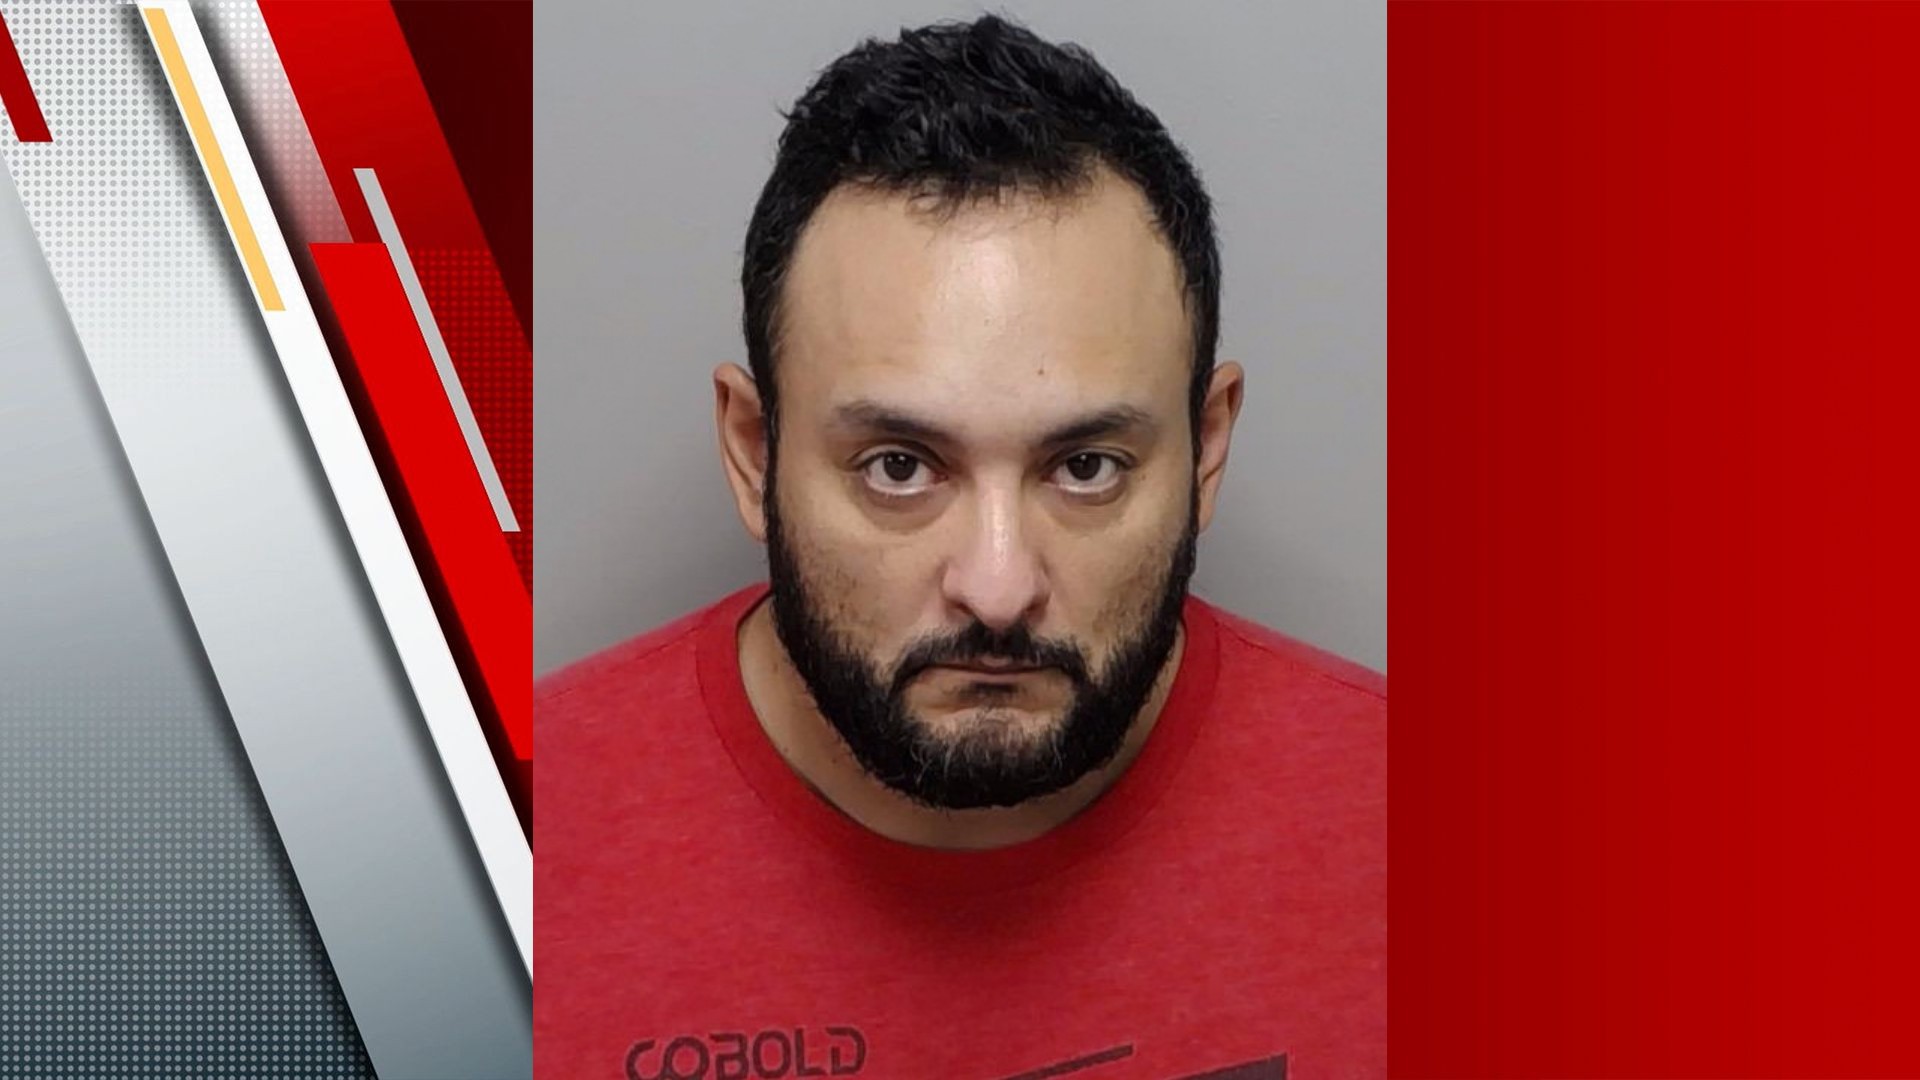
A Texas man is in federal custody after authorities say they disrupted an alleged plot to carry out a shooting at the Texas State Capitol—just one day before President Donald Trump was scheduled to visit the state.
Benny Caldera Jr., 40, of Converse, was initially arrested early Wednesday on a felony charge of making a terroristic threat against a public servant after investigators received what authorities described as “credible information about an individual planning a violent attack.”
According to an arrest affidavit cited by NBC 5, a friend told investigators that Caldera had threatened to shoot up the Texas Capitol and made alarming statements about people associated with the American Israel Public Affairs Committee, or AIPAC.
The friend reportedly told investigators that Caldera said people associated with the prominent pro-Israel organization needed to be exterminated.
Authorities say the alleged attack was planned for Thursday, Oct. 1—the same day Trump was scheduled to visit Texas.
The warning set off an overnight law-enforcement operation.
The Texas Department of Public Safety said it received information about the alleged plot Tuesday evening and immediately began working with the FBI and local authorities.
Investigators worked through the night.
By approximately 3 a.m. Wednesday, SWAT officers had moved in on Caldera’s Converse home and taken him into custody.
He was booked into the Bexar County Jail on the state terroristic-threat charge, with bond initially set at $75,000.
But Caldera wasn’t going home.
After reports circulated suggesting he had been released on bond, DPS publicly pushed back, saying he remained in custody.
The FBI then arrested Caldera at the jail Wednesday evening on additional federal charges connected to the alleged plot, according to DPS.
He was transferred into federal custody.
“The department said he is not out on bond,” according to the account of the case.
The specific federal charges against Caldera had not yet been publicly disclosed.
NBC 5 also reported that Bexar County court records show Caldera was previously charged with unlicensed carrying of a weapon in November 2023. The reported account did not provide the ultimate disposition of that case.
News of the alleged plot quickly reached state lawmakers.
Texas legislators were notified Wednesday about both the threat and Caldera’s arrest as authorities increased security around one of the state’s most prominent government buildings.
Despite the alleged threat, the Texas State Capitol remained open during its normal operating hours with heightened security measures in place.
Authorities stressed that they do not currently believe the public remains in danger.
DPS said there is no reason to believe an ongoing threat exists against the Capitol, lawmakers, employees or members of the public.
The investigation remains active.
The timeline, however, underscores how quickly authorities say the situation escalated: investigators received information about an alleged violent attack Tuesday evening, worked through the night and had a suspect in custody by approximately 3 a.m.
Hours later, the FBI stepped in and took Caldera into federal custody.
The alleged target was the Texas State Capitol.
And according to authorities, the planned date was Oct. 1—the same day a sitting president was scheduled to visit the state.
A Department of Energy electrical engineer has been arrested on a stunning federal terrorism charge after investigators accused him of attempting to help the Iran-backed Houthis with technical expertise, drone components and materials associated with the production of explosives.
Ashton Hamed Ellaboudy, 51, of Richland, Washington, was arrested Thursday and charged with attempting to provide material support or resources to a designated foreign terrorist organization.
Federal prosecutors allege Ellaboudy was employed by the Department of Energy while using his specialized electrical engineering knowledge in an effort to assist the Houthis.
The allegations immediately drew a blistering response from the Justice Department.
“As alleged, a U.S. government employee traveled overseas and used his specialized expertise in an attempt to aid the Houthis, a designated Foreign Terrorist Organization backed by Iran,” said Assistant Attorney General for National Security John A. Eisenberg. “Additionally, Ellaboudy acquired materials for the construction of explosive material and drones capable of delivering these explosives. These allegations are so deeply disturbing that they almost defy imagination.”
According to the criminal complaint, the FBI’s investigation began after authorities learned Ellaboudy had allegedly purchased precursor chemicals, components and other materials commonly associated with homemade explosive devices.
Investigators also discovered purchases of components used to build drones and remotely operated aerial systems, prosecutors said.
But the allegations extend far beyond purchases made inside the United States.
Federal authorities say Ellaboudy traveled from Washington state to Oman in September 2025 before crossing into Yemen using an official passport previously issued to him while he worked for the U.S. Army Corps of Engineers.
According to a release from the U.S. Department of Justice, a 51 year old former employee of the Department of Energy, Ashton Hamed Ellaboudy, was arrested and charged with attempting to provide material support to the Yemeni Houthis, who are a designated terrorist organization.… pic.twitter.com/lhySGgETbV
— OSINTdefender (@sentdefender) October 1, 2026
According to the FBI, Ellaboudy intended to reach Sanaa, Yemen’s Houthi-controlled capital.
He ultimately failed to make it there.
When Ellaboudy returned to the United States, prosecutors allege he told Customs and Border Protection officers that his overseas trip had been official government business.
Investigators say that story didn’t hold up.
Ellaboudy’s Department of Energy supervisor later told authorities that he had no authorized government travel to the region and had not been assigned to the missile inspection mission Ellaboudy allegedly described, according to court records.
Federal investigators further allege Ellaboudy admitted to FBI informants that he had been smuggled into and out of Yemen and hoped to establish high-level connections inside the country.
The investigation then took another turn.
Ellaboudy began communicating with an FBI confidential source who purported to be working for a Houthi “Colonel,” according to prosecutors.
Authorities allege Ellaboudy subsequently put his engineering expertise to work.
He allegedly helped test and modify solar power generators and communications equipment intended for a mobile communications center.
Prosecutors say he also supplied diagrams, technical guidance and research involving equipment that could potentially enhance Houthi communications capabilities.
Investigators have also scrutinized Ellaboudy’s previous acquisition and handling of chemicals.
The Justice Department said authorities learned that in 2024 Ellaboudy took sick leave from his government position after reporting exposure to highly concentrated nitric acid.
Nitric acid has legitimate industrial and scientific applications but can also be used in producing certain explosive materials.
Taken together, federal prosecutors allege the engineer’s activities amounted to an attempt to provide material support to the Houthis.
The Houthis, formally known as Ansar Allah, control significant portions of Yemen and have received support from Iran. The United States has designated the organization as a foreign terrorist organization.
Ellaboudy now faces up to 20 years in federal prison if convicted.
The case puts a particularly striking element at the center of the government’s allegations: prosecutors aren’t accusing an ordinary private citizen of simply attempting to make contact with a foreign terrorist organization.
They allege a U.S. government engineer attempted to use specialized technical expertise—and acquire materials involving drones and explosives—to help one.
Ellaboudy has been charged, not convicted, and is presumed innocent unless and until proven guilty in court.
Former Republican Congresswoman Patricia “Pat” Saiki, a trailblazing Hawaii lawmaker who made history as the first Republican elected to represent the state in the U.S. House following statehood, has died at 96.
Saiki died of natural causes at her Honolulu home on September 30, according to her son, Stuart Saiki.
Her death closes a remarkable chapter in Hawaii politics spanning decades and encompassing service in Congress, the state legislature and the administration of President George H.W. Bush.
Born Patricia Fukuda in Hilo on May 28, 1930, Saiki graduated from Hilo High School before earning her degree from the University of Hawaii in 1952.
Politics wasn’t initially her chosen career.
Saiki began as an educator, teaching at several schools before becoming involved in organizing Hawaii’s first teachers’ union.
Her move into elected office came in 1968, when she won a seat in the Hawaii House of Representatives.
She served there for six years before winning election to the state Senate in 1974, where she remained until 1982.
Following an unsuccessful campaign for lieutenant governor, Saiki took over as chairwoman of the Hawaii Republican Party and worked to expand the party’s membership in a state that was already becoming increasingly difficult terrain for Republicans.
Then came the breakthrough that would define her political legacy.
In 1986, Saiki won election to Congress, becoming the first Republican elected to the U.S. House from Hawaii since the islands became a state in 1959.
She was also only the second woman to represent Hawaii in Congress.
Her death prompted tributes from across Hawaii’s political establishment.
Gov. Josh Green ordered American and state flags lowered to half-staff beginning Friday, October 2, through sunrise Monday, October 5.
“Pat Saiki’s six decades of public service and her pioneering example for young women and Asian Americans in Hawaiʻi and across the U.S., combine to form both a lasting, inspiring legacy and a high bar for all of us who serve the public,” Green said in a statement.
Democratic Rep. Ed Case, who represents Hawaii’s 1st Congressional District, also paid tribute to Saiki, crediting her with breaking political barriers and establishing an example for future generations of public servants.
Saiki’s impact extended far beyond her historic election.
During her two terms in Washington, she helped secure Republican support for legislation authorizing an official apology and financial compensation for Japanese Americans incarcerated by the federal government during World War II.
She also became an advocate for environmental protections in Hawaii.
In 1990, Saiki successfully urged President George H.W. Bush to halt the U.S. Navy’s use of Kahoʻolawe as a military bombing range.
Her career in Washington took another turn that same year when she left the House to challenge Democrat Daniel Akaka for a U.S. Senate seat.
Saiki lost the race, but her federal service wasn’t finished.
Bush subsequently appointed her administrator of the Small Business Administration, where she served from 1991 until 1993.
She later taught at Harvard University’s Institute of Politics before returning to Hawaii politics for another statewide campaign.
In 1994, Saiki ran unsuccessfully for governor against Democrat Ben Cayetano.
Although a Republican, Saiki maintained moderate positions on several social issues, including abortion rights, and developed a reputation for working across party lines on legislation affecting Hawaii.
Behind the political milestones was also a mother raising five children.
Her son Stuart remembered Saiki as someone who refused to allow the demands of public office to completely overtake her responsibilities at home.
Even while serving in the legislature, he recalled, she continued helping her children with homework and handling the responsibilities of raising a family.
Saiki was preceded in death by her husband, Stanley, and their eldest son, Stanley Jr.
She is survived by four children—Stuart, Sandra, Margaret and Laurie—as well as her grandchildren.
Saiki’s career ultimately stretched from Hawaii classrooms to the state legislature, from Capitol Hill to a presidential administration.
But her place in Hawaii political history was secured in 1986.
Nearly three decades after Hawaii entered the Union, Patricia Saiki accomplished something no Republican before her had managed in the new state: win election to represent Hawaii in the United States House of Representatives.
She was 96.

JUST IN: Horrific Terror Plot Targeted At Trump THWARTED

Trump Admin Caught Colluding With Iran-Backed Terrorists

First Republican Congresswoman From Deep Blue State Dead

Dems Revolt Against Schumer And Side With Trump

Charlie Kirk’s Mother Breaks Her Silence After Erika Kirk’s Public Statement

Jaw-Dropping Details Emerge From Hijacking Attempt On Israel-Bound Flight

‘The Five’ Gets Emotional As Greg Gutfeld Announces Tragic News

Joe Biden’s Daughter Just Dropped Massive Public Bombshell On Her Dad

Obama Calls It QUITS After Wild Video Goes Viral

Removed From the Country — Ilhan Omar Hit With Horrid News

Get Ready — Mike Pence Makes Stunning 2028 Announcement

Schumer Loses! Court Sides With Trump In Historic Move
-
 Economy6 months ago
Vance Leaves Meeting, Looks Straight Into Camera, Announces Stunning Arrest
-
 Economy6 months ago
Adam Schiff Facing 30 Years In Prison After Bank Records Leak
-
 Economy6 months ago
Supreme Curt Sides With Trump — He Can Remove The All
-
 Culture4 months ago
Michelle Obama Drops Nasty Bomb About ‘Useless’ Daughter
-
 Economy6 months ago
All Hell Breaks Loose On Fox When Jesse Watters Asks Fetterman One Question
-
 Economy4 months ago
Prayers Pour In After Fox Host Dies: ‘Senseless Murder’
-
 Latest4 months ago
Fox News Stuns With Announcement About 5 Fired Hosts
-
 Border & Security2 months ago
Top Trump Admin And Wife Found Dead — Chilling Update Just Released