Latest
Anthropic’s Mythos AI found over 2,000 unknown software vulnerabilities in just seven weeks of testing

There is a new AI model called Mythos. Anthropic built it for defensive cybersecurity research. It is so effective at finding software vulnerabilities that Anthropic decided the general public cannot have it. Instead, they are letting a small circle of trusted partners like Microsoft and Google experiment with it first, under controlled conditions, while researchers figure out what guardrails need to exist.
That decision alone should tell you something. When the company that built a tool decides the world is not ready for it, you pay attention. And when you understand what Mythos actually did during testing, that caution starts to make complete sense.
Sign up for my FREE CyberGuy Report
WINDOWS PCS AT RISK AS NEW TOOL DISARMS BUILT-IN SECURITY
Seven weeks. One AI model. One team. More than 2,000 previously unknown software vulnerabilities were found. If you need a moment with that, take it. John Ackerly, CEO and Co-Founder of Virtru, a data security company, put that figure into perspective in a way that is hard to shake.
“Mythos is absolutely a turning point for cybersecurity. Think about it. Mythos didn’t pick a lock; it found thousands of locks that were never locked in the first place (that no one even knew existed) in software that the best human security researchers had studied for decades.
The math is staggering. One AI model, and one team, in seven weeks, found more than 2,000 zero-day vulnerabilities. That is 30% of the world’s entire annual output prior to AI. When thousands of researchers get access to AI models like Mythos, a single year will surface exponentially more zero-days than the 360,000 recorded in all of software history.
Mythos and other AI models like it can now find and exploit software flaws at a speed and scale that is beyond containment. This means that the old approach of building stronger walls around systems and hoping they hold is becoming much less reliable. It also means that the manual ‘find a vulnerability, patch the vulnerability’ process is not going to keep pace with a threat landscape bolstered by the speed and scale of AI.
The threat surface is now expanding faster than any wall can contain it. The only answer to this new dynamic is to protect the data itself, rather than prop up perimeter protection around it.”
Thirty percent of the world’s annual output in seven weeks changes the game entirely.
Cybersecurity teams have used AI tools for years. So what makes this different?
Ackerly explains it this way: “What makes this different is the level of autonomy and speed it enables. Mythos is being described as a system that can discover vulnerabilities and even generate working exploits much faster than traditional human-led workflows. This model could make it easy for a bad actor to identify and exploit vulnerabilities in software, even if that bad actor isn’t knowledgeable or trained.”
That last part matters most. Before a tool like this, exploiting a serious software vulnerability required real technical skill. Mythos AI lowers that barrier significantly. A person with bad intentions and no technical background could potentially use a model like this to cause serious damage. The expertise gap that once offered some natural protection is closing.
FAKE PAYPAL EMAIL LET HACKERS ACCESS COMPUTER AND BANK ACCOUNT
Most cybersecurity spending, the overwhelming majority of it, goes toward what experts call perimeter defense. Think firewalls, network monitoring, endpoint security and intrusion detection. The entire strategy is built on one core idea: keep the bad actors out, and the data inside stays safe.
Ackerly describes how that model is now breaking down.
“The perimeter is the digital wall around your systems and the information you possess. For decades, cyber strategies have primarily focused on the idea that if you protected the perimeter well enough – if you built a strong enough wall – the sensitive data on the inside would stay safe. The industry has poured hundreds of billions of dollars into firewalls, endpoint detection, network security, application security, and other perimeter defenses.
Traditional security architecture by itself cannot keep pace in this new world.
The Mythos development from Anthropic is making a hard truth very apparent: time is running out for companies to prepare for this new reality. Shifting focus from ‘protecting the perimeter’ to ‘protecting the data’ is critically important to mitigate data loss or compromise.”
Hundreds of billions of dollars. And now the model those dollars were built on is becoming unreliable. It forces a full rethink.
This is the question everyone wants a straight answer to. Ackerly offers one that is more nuanced than a simple yes or no.
“I wouldn’t frame it as attackers automatically having an advantage. But over time, it does mean that ‘bad guys’ and ‘good guys’ will have access to essentially the same tools. As a result, I do think defenders absolutely need a different strategy. If you assume the outer wall may fail, then the smarter move is to protect the data itself so it stays controlled even after a breach.”
The playing field is leveling. And that may sound fair until you remember attackers only need to succeed once, while defenders have to succeed every time.
Speed is what makes Mythos AI genuinely alarming. Traditional cyberattacks move through a lifecycle. Reconnaissance takes time. Finding the right vulnerability takes more time. Building an exploit takes more time on top of that.
Ackerly explains what happens when AI compresses all of that.
“AI is accelerating the threat. A model that can find and exploit vulnerabilities autonomously compresses the attack lifecycle from weeks to hours, or even minutes. Every layer of the traditional security stack now has to operate at machine speed. Manual security architectures cannot keep up.
But AI also makes data-centric security more powerful, not less so. When every piece of sensitive data is protected at the object-level, AI agents can enforce governance at scale by checking entitlements, applying attribute-based access controls, and auditing data flows in real time. The same capabilities that make Mythos a dangerous tool in the hands of ‘bad guys’ make it a valuable tool in the hands of ‘good guys’.
The question organizations should be asking shifts from “how do I build higher walls?” to “when the walls fail, is my data still protected?” That is the question worth sitting with.
Most of the Mythos coverage has focused on corporate risk. But your bank account and medical records sit in those same vulnerable systems.
“For everyday people, the first change is that breaches and scams could become more frequent, more targeted, and harder to spot. If AI makes it easier to uncover weak points in the systems we all rely on, that can translate into more pressure on the services that hold our personal data, from email and cloud storage to health, banking, and retail platforms.
Consumers shouldn’t assume a company is doing the right thing with their data. Now, they really can’t assume a company’s outer defenses are enough to protect their information.
This also highlights the importance of basic cyber hygiene like unique passwords and MFA, so that when breaches happen, the scope of impact on your own personal data is contained.”
Your bank account, your medical records, your tax documents, your private messages. All of it already lives across dozens of platforms you trust to protect it. If those platforms’ outer defenses are no longer reliable, what exactly is standing between your data and someone who wants it?
Ackerly goes further on where the exposure actually lives. “Data now travels across clouds, devices, partners, and borders. The risk isn’t just one hacked server in one building anymore. It’s all the places your data passes through or gets copied to along the way.
Anthropic made a choice that is rare in the AI industry. They built something powerful and then decided not to release it widely.
On that decision, Ackerly is direct. “Anthropic’s decision to withhold Mythos from general release is unprecedented and, frankly, responsible. Time will tell what these partners are able to do with regard to safety, but releasing it to the general public would certainly have been ill-advised and dangerous.”
Unprecedented. That word deserves weight here. In an industry that races to release new tech, Anthropic stopped. That speaks volumes.
We reached out to Anthropic for a comment, but did not hear back before our deadline.
THIRD-PARTY BREACH EXPOSES CHATGPT ACCOUNT DETAILS
The perimeter model is deteriorating, but that does not mean you are helpless. Individual behavior still matters, and it matters more now than it did before.
Ackerly’s recommendation is this: “Stop assuming the app, platform, or company perimeter can always protect your information, or that they will do the right thing with your data. People should be much more deliberate about what data they share, where they store it, and who can access it. Protection needs to travel with the data, not just sit at the edge of a network. For you, that means choosing services that give you stronger control over your information and being more cautious about oversharing sensitive data in the first place. The data owner should always have governance over said data.” So where do you start?
A password manager makes this realistic. If one platform gets breached, unique passwords keep the damage isolated to that one account.
Multi-factor authentication (MFA) adds a layer that survives even when a password is compromised. It is one of the highest-impact steps an individual can take.
Outdated software is one of the most common entry points attackers use. Strong antivirus software catches threats your instincts might miss, and keeping apps and operating systems current closes the gaps that models like Mythos are built to find. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android & iOS devices at Cyberguy.com
Every app that holds your data is a potential exposure point. The less you overshare, the smaller your footprint becomes.
Data brokers collect and sell your personal information, often without you ever knowing. Data removal services find where your data is listed and request its removal. You cannot control every place your information travels, but you can shrink the trail it leaves behind. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting Cyberguy.com
Not all platforms treat your data the same way. Look for services that let you see, manage and limit how your information is used and where it goes.
Catching a breach early limits the damage significantly. Set up account alerts wherever your bank or financial platform allows it. A credit freeze costs nothing and stops new accounts from being opened in your name without your knowledge.
Ackerly warned that scams will get more targeted and harder to spot as AI lowers the barrier for bad actors. Scrutinize every link before you click it and treat unexpected emails or texts asking for login information as suspicious by default. If something feels off, it probably is.
The goal is to limit how much damage they can do. When you operate with that assumption, your decisions about data hygiene get sharper, and your exposure gets smaller.
Take my quiz: How safe is your online security?
Think your devices and data are truly protected? Take this quick quiz to see where your digital habits stand. From passwords to Wi-Fi settings, you’ll get a personalized breakdown of what you’re doing right and what needs improvement. Take my Quiz here: Cyberguy.com
Mythos did not create the vulnerability problem. It made the scale of it visible in a way that is no longer ignorable. The foundation of modern cybersecurity, the idea that strong enough walls will keep data safe, is being tested in real time by a technology that moves faster than any human team can. That is a consumer story as much as it is a corporate one. Your data lives in systems built on that old model. And the moment to think differently about how it is protected is now, not after the next major breach makes the headlines. Anthropic made a responsible call by limiting access to Mythos. But the model exists. The capability is real. Other versions of it are being developed. The question for every organization and every individual becomes the same one Ackerly keeps returning to.
When the walls fail, and experts are telling us they will, what is actually protecting your data on the other side? Let us know your thoughts by writing to us at Cyberguy.com
Sign up for my FREE CyberGuy Report
Copyright 2026 CyberGuy.com. All rights reserved.
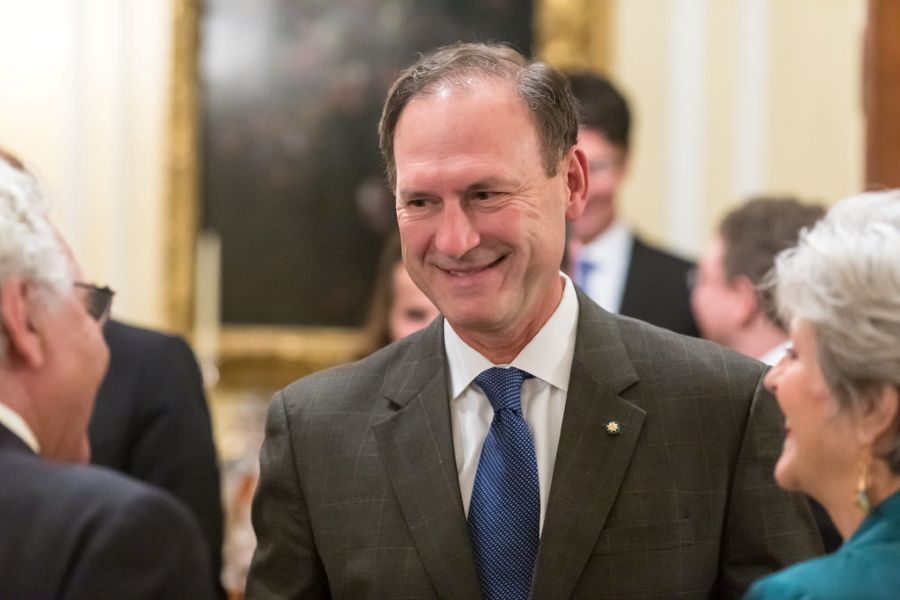
Supreme Court Justice Samuel Alito has abruptly withdrawn from one of the most consequential climate-related cases before the high court, leaving just eight justices to decide a dispute that could affect lawsuits seeking billions of dollars from fossil-fuel companies.
The court notified attorneys Monday that Alito “has determined that he will not continue to participate” in *Suncor Energy Inc. v. County Commissioners of Boulder County*.
No explanation was provided for his decision.
The last-minute development comes ahead of arguments in a closely watched Colorado case that could have implications for similar climate lawsuits brought by states and municipalities across the country.
The dispute dates back to 2018, when Boulder County and the City of Boulder sued Exxon Mobil and Suncor Energy in Colorado state court. San Miguel County later joined the litigation.
The municipalities allege the companies contributed to “climate-related harms” through decades of fossil-fuel production, refining and sales, along with what the plaintiffs describe as “concealment or misrepresentation” concerning the risks associated with their products.
They are seeking damages under Colorado state law for costs they attribute to climate change, including flooding, wildfire risks, drought and damage to public infrastructure.
The energy companies argue that the claims cannot proceed under state tort law because federal law governs interstate air pollution and because allowing individual states to regulate conduct tied to global emissions raises constitutional concerns.
After years of litigation over where and how the case could proceed, the Colorado Supreme Court allowed the lawsuit to move forward.
The U.S. Supreme Court subsequently agreed to hear the dispute.
The stakes extend far beyond Colorado.
Similar lawsuits have been filed against fossil-fuel producers by states and local governments seeking compensation for climate-related costs. The Supreme Court’s eventual decision could therefore shape how those cases proceed.
Alito’s withdrawal is particularly notable because he previously recused himself from an earlier petition arising from the same Colorado litigation in 2023.
He has also stepped aside from other energy-related cases.
When the Supreme Court agreed to hear the current Suncor appeal, however, a court spokesperson said in May that Alito “does not have a financial interest in any party” and that the court’s legal counsel had determined recusal was not required.
Alito does not own stock in Exxon Mobil or Suncor.
His most recent financial disclosure does list individual investments in other energy companies, including ConocoPhillips and Phillips 66, which are defendants in separate climate-related litigation.
Advocacy groups had argued that those investments, combined with the potential industry-wide implications of the Suncor case, raised questions under the Supreme Court’s Code of Conduct.
The code states that a justice should recuse when the justice’s impartiality might reasonably be questioned or when the justice has a financial interest in the subject matter in controversy.
But justices generally are not required to explain why they recuse themselves, and Alito has not publicly stated what prompted his decision in this case.
His absence could have a significant procedural consequence.
Only eight justices will now participate. If the court divides 4-4, the Colorado Supreme Court’s ruling would remain in place without establishing a nationwide Supreme Court precedent.
The remaining court includes five conservative justices and three liberal justices, although ideological alignment does not necessarily determine how individual justices will approach the federal-preemption questions presented in the case.
Alito had been viewed by some legal observers as potentially receptive to the companies’ argument that federal law prevents states from using their own tort laws to impose liability over emissions associated with global climate change.
His decision to step aside removes one vote from the case before arguments even begin.
What remains unexplained is why.
The court’s notification says only that Alito “has determined that he will not continue to participate,” leaving the reason for his withdrawal undisclosed as the justices prepare to hear a case with potential consequences for climate litigation nationwide.
Five men have been arrested in a suspected terror plot near one of America’s most strategically important bomber hubs in Britain, triggering an intensive counterterrorism investigation and renewed security concerns surrounding U.S. military installations overseas.
British authorities launched the investigation after police received a report shortly before 1 a.m. Sunday about three suspicious vehicles apparently traveling toward RAF Fairford.
Armed officers descended on the nearby Whelford area and arrested five men initially on suspicion of explosives offenses. Authorities subsequently arrested the suspects on suspicion of preparing a terrorist act under Section 5 of Britain’s Terrorism Act.
All five are British nationals from London in their early twenties, police said Monday.
Investigators are now working to determine what the men allegedly intended to do, their motive and whether anyone else — including a foreign actor — played a role.
RAF Fairford is owned by Britain but serves as a strategically important operating location for the U.S. Air Force, including American long-range bombers.
The installation has taken on increased importance amid U.S. military operations involving Iran and the broader Middle East.
Former Defense Intelligence Agency official Andrew Badger said the circumstances surrounding the arrests immediately stood out.
Five suspects traveling in three separate vehicles, he argued, could indicate investigators are dealing with something more coordinated than an isolated individual.
“This isn’t just some type of amateur lone wolf operation,” Badger told Fox News Digital while discussing the investigation.
Badger also predicted the incident could lead to tougher security measures at American military facilities.
“We are going to see elevated security protocols,” he said.
The potential target is significant.
American B-1B Lancers and B-52 Stratofortresses have operated from RAF Fairford, providing the United States with a European location capable of supporting long-range strategic bomber missions.
Its reinforced runway stretches nearly two miles and is capable of handling some of America’s largest military aircraft.
President Donald Trump addressed the arrests Sunday and said American and British authorities had worked together in connection with the incident.
“They were looking to do big damage to our fort,” Trump told reporters.
Trump also praised cooperation between the United States and Britain following the arrests.
British authorities have been considerably more cautious about assigning a motive.
Investigators are still trying to establish what happened and why. Possible foreign involvement is reportedly among the avenues being examined, but authorities have not publicly concluded that Iran — or any other government — directed the alleged plot.
Iran’s embassy in London denied involvement Monday amid speculation surrounding the arrests.
Investigators are reportedly examining several possible motives, including potential Iranian links, Russian sabotage and Islamist extremism. None of those possibilities has been publicly established as the cause of the suspected plot.
The Iranian connection has drawn particular attention because of recent tensions surrounding military installations supporting operations against Tehran.
Iran’s Islamic Revolutionary Guard Corps warned in July that bases supporting attacks against Iranian territory could become military targets.
Britain had previously authorized American forces to use Fairford for certain operations against Iranian missile positions.
Security around the installation had reportedly already been increased.
Local councilor Tristan Wilkinson told Reuters that surveillance was stepped up following a specific Iranian threat roughly six weeks before Sunday’s arrests.
Authorities have not publicly established any connection between that earlier threat and the five suspects.
The response on the ground was substantial.
Approximately 85 households were evacuated while authorities established a roughly 400-meter security cordon as specialists examined vehicles connected with the investigation.
Reports indicated that a local farmer alerted authorities after spotting three large white vans and suspicious activity near the military installation. Hooded and masked individuals were reportedly seen running toward nearby fields.
Former Trump White House official Morgan Murphy said American agencies would likely be working closely with British investigators as authorities attempt to determine whether the alleged operation extended beyond the five suspects.
Murphy pointed to Air Force investigators, U.S. intelligence personnel and FBI officials stationed in London as among those who could become involved.
Investigators are likely to examine communications, financial transactions and other records for evidence of additional connections, he said.
The area contains another strategically important American military facility as well.
Nearby RAF Welford houses a major U.S. weapons and ammunition storage operation supporting American forces in Britain and across the European theater.
For now, the most important questions remain unanswered: what the five men allegedly planned, whether RAF Fairford was their intended target, and whether anyone else was behind them.
British counterterrorism authorities continue to investigate, and no foreign government or organization has been publicly identified by police as responsible for the suspected plot.
Republicans were dealt a surprise blow in one of Pennsylvania’s most reliably red state House districts after Democrat Brandon Dukes pulled off a razor-thin special-election upset in territory President Donald Trump carried by more than 18 points.
But the fight isn’t over.
Dukes defeated Republican Scott Timko by just 88 votes in Pennsylvania’s 12th House District in Butler County, flipping a seat Republicans had controlled for decades.
Now Republicans will get an immediate opportunity to take it back when Dukes and Timko face each other again in November.
The special-election result immediately drew attention because of just how Republican the district has historically been.
Trump carried the district by more than 18 percentage points in the 2024 presidential election, while former Republican state Rep. Stephenie Scialabba won the district by roughly 30 points that same year.
Scialabba’s resignation earlier this year created the vacancy and triggered the special election.
Dukes’ victory broke a Republican hold on the seat dating back decades and gave Democrats a significant pickup just months before the November midterms.
But Republicans are pointing to one major factor that could make the rematch very different: turnout.
Participation in the special election was unusually low, producing an electorate far smaller than the one expected to vote in November.
That leaves both parties preparing for a dramatically different contest when a much larger group of voters returns to the polls for the general election.
The Pennsylvania House Republican Campaign Committee made clear that it considers Tuesday’s result only the first round.
“The General Election starts today with Scott Timko reaching out to voters, building a winning coalition, and holding Brandon Dukes accountable for his extreme positions that he continues to hide from voters.”
The special-election reporting did not specify which positions Republicans were referring to.
Pennsylvania House Republican Leader Jesse Topper also sought to put the loss in perspective, describing the result as “disappointing but unsurprising” while pointing to changing demographics, the summertime election date and the unpredictable nature of special-election turnout.
“There is much more yet to unfold in the final months of the 2026 election cycle and we will continue carrying out vision for positive growth in Pennsylvania through November,” he said.
The district itself underscores why the result is attracting attention.
Pennsylvania’s 12th House District covers portions of Butler County north of Pittsburgh, including Cranberry, Adams and Jackson townships and several surrounding communities. Republicans also hold a substantial voter-registration advantage in the district.
Yet Dukes managed to overcome those structural advantages in the low-turnout special election and capture the seat by fewer than 100 votes.
The result gives Democrats control of a district that had long been considered safe Republican territory — at least for now.
Republicans will have their chance to reverse the upset on November 3, when Timko and Dukes meet again to determine who will represent the district for a full two-year term beginning in 2027.
With the special election decided by only 88 votes, the rematch is shaping up to be a closely watched Pennsylvania House contest heading into November.

NEW: Justice Alito Abruptly Reverses Course In Key SCOTUS Case

National Emergency Declared — Trump Called In

Seat Officially Flipped After HUGE Win and Election Upset

ALERT: Trump Set To Make ‘Special Announcement’ From Oval Office

CEO Charged In Scheme To Infiltrate Secret Service

Trump Torches Supreme Court Over Controversial New Ruling

‘The Five’ Gets Emotional As Greg Gutfeld Announces Tragic News

Joe Biden’s Daughter Just Dropped Massive Public Bombshell On Her Dad

Removed From the Country — Ilhan Omar Hit With Horrid News

Obama Calls It QUITS After Wild Video Goes Viral

Get Ready — Mike Pence Makes Stunning 2028 Announcement

Schumer Loses! Court Sides With Trump In Historic Move
-
 Economy6 months ago
Vance Leaves Meeting, Looks Straight Into Camera, Announces Stunning Arrest
-
 Economy6 months ago
Adam Schiff Facing 30 Years In Prison After Bank Records Leak
-
 Economy6 months ago
Supreme Curt Sides With Trump — He Can Remove The All
-
 Culture3 months ago
Michelle Obama Drops Nasty Bomb About ‘Useless’ Daughter
-
 Economy6 months ago
All Hell Breaks Loose On Fox When Jesse Watters Asks Fetterman One Question
-
 Economy4 months ago
Prayers Pour In After Fox Host Dies: ‘Senseless Murder’
-
 Latest3 months ago
Fox News Stuns With Announcement About 5 Fired Hosts
-
 Border & Security2 months ago
Top Trump Admin And Wife Found Dead — Chilling Update Just Released